IT Infrastructure
CodeQL 2.27.4 shows why a changing alert count needs an explanation
A security report shows fewer findings than it did last week, but nobody has changed the affected code. Is that progress? CodeQL's latest update offers a useful example of why the answer depends on what the scanner now recognizes and how it groups the results.
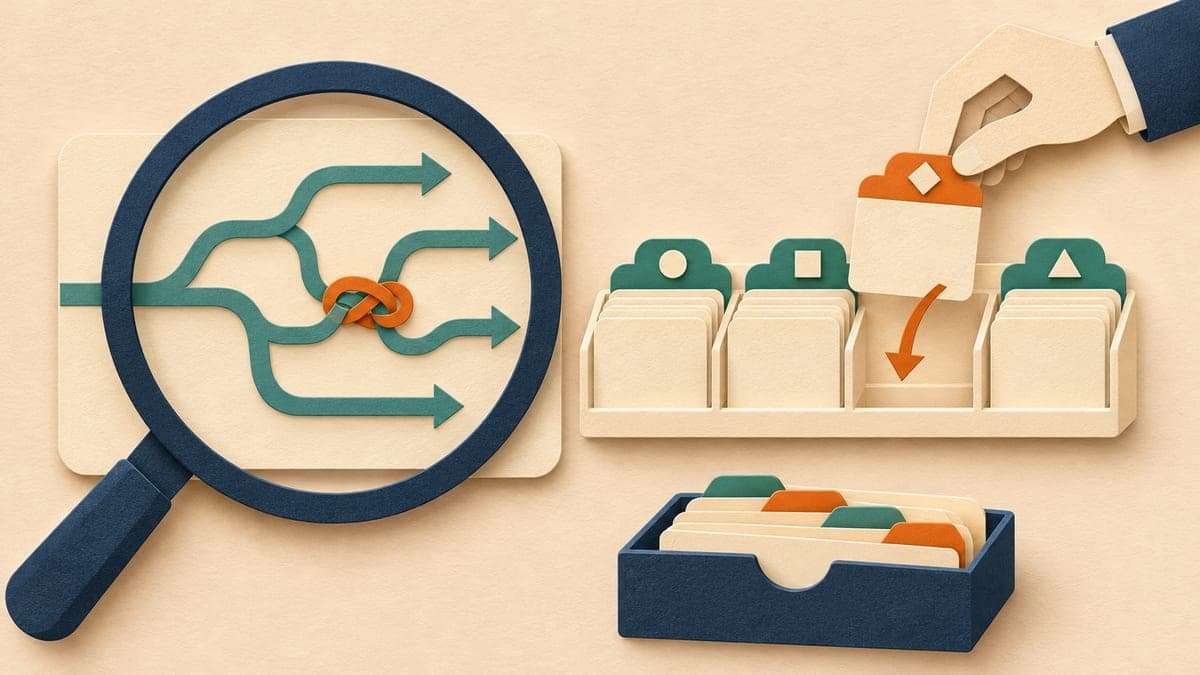
More precise analysis can change the result
GitHub's November 4 changelog highlights CodeQL 2.27.4, whose release notes are dated November 2. CodeQL powers GitHub code scanning. This update includes query-accuracy improvements, revised metadata and command-line safeguards.
GitHub reports fewer false positives in several Rust queries. Java/Kotlin analysis recognizes additional sanitizers and guards in common libraries. For C++, intentional arithmetic on byte buffers and variables explicitly marked as possibly unused receive more accurate handling.
Those examples explain why an alert can disappear after a tool update without a corresponding application fix. A scanner recognizing an existing safeguard is different from a developer adding a new safeguard. Neither a lower total nor an unchanged total establishes that the whole application is safe.
Classification changes deserve their own line in the report
The release notes also remove the CWE-730 tag from selected queries across several languages because MITRE has prohibited that weakness identifier for vulnerability mapping. The affected queries retain their other CWE tags.
For a team grouping findings by weakness category, that is a reporting distinction worth preserving. A category's count might change even when the underlying code has not. A dashboard that only displays totals can hide that distinction.
A useful comparison records the scanner version, query suite and application revision alongside the result. In a hypothetical review, a team can separate findings affected by revised tagging from findings whose code paths actually changed. That makes the discussion more concrete than describing every reduction as remediation.
The command-line changes affect the evidence pipeline
CodeQL 2.27.4 moves Java virtual-machine warnings and initialization errors to standard error so they do not corrupt JSON or other machine-readable command output. It also checks files when bundling or publishing query packs: after resolving symbolic links, files outside the pack root are omitted with a warning.
For teams processing scan results automatically, the practical implication is to examine both structured output and diagnostic messages. A parser receiving valid JSON and a pack containing its intended files are separate checks. A successful-looking summary alone should not answer both questions.
These changes do not justify silencing warnings or assuming that every older result was wrong. They provide specific behaviors to test in an existing analysis workflow, without turning a tool release into a claim about any particular repository.
Keep the comparison like for like
GitHub's query-suite documentation distinguishes the default suite from security-extended. The latter adds queries with somewhat lower precision and can return more false positives. Switching suites while updating the scanner makes a simple before-and-after alert total harder to interpret.
An operational review can first compare the same code revision and suite, then inspect representative changed findings. A separate comparison can evaluate code fixes or a deliberate expansion of coverage. Keeping those questions separate helps a team explain its workload without claiming a measured reduction in risk that the evidence does not establish.
Sources
What to watch
A useful report explains the difference
The business value of a scanner update is easier to assess when the report identifies what changed in the tool, what changed in the code and what still needs investigation. A smaller total can be informative, but the explanation matters more than the direction of the number.